Critical infrastructure (KRITIS) is essential to the functioning of society. For this reason, the organisations and facilities involved are subject to strict regulatory requirements. TÜV Nord supports you in meeting all these requirements with its KRITIS certification services.
Request Offer

Critical infrastructure (KRITIS) comprises facilities, installations, systems and associated organisations that are essential to the functioning of society, public safety and the provision of services to the population.
KRITIS provide critical services, and measures must be taken to prevent failures or disruptions to these infrastructures.
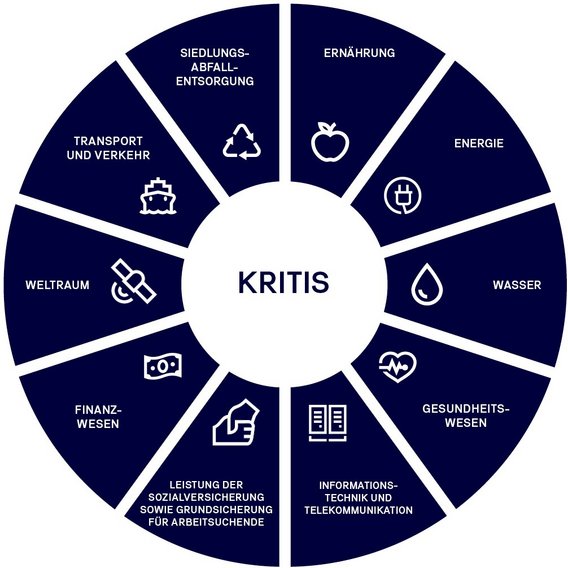
Originally, nine sectors fell under KRITIS; following the 2021 amendment to the Act on the Federal Office for Information Security (BSIG), there are now ten sectors and industries:
Whether a facility is classified as KRITIS depends on its type, size and significance within the relevant sector. Key factors include the number of people served and sector-specific thresholds.
At federal level, these thresholds are laid down in the KRITIS Framework Act (KRITISDachG), which came into force in March 2026. According to this, all facilities that serve 500,000 people are, in principle, considered critical infrastructure. However, under Section 5(5) of the KRITIS Framework Act, the federal states may also designate facilities that do not meet these thresholds.
The Federal Ministry of the Interior is currently working on amending the Ordinance on the Designation of Critical Facilities under the KRITIS Framework Act (BSI-Kritis Ordinance, BSI-KritisV), which sets out the sector-specific thresholds and classification criteria in detail.
KRITIS operators must meet numerous requirements regarding the information security and resilience of their facilities in accordance with the BSIG and the KRITISDachG. In addition, there are sector-specific regulations. These require, amongst other things:
Registration must take place no later than three months after classification as critical infrastructure. The necessary security and resilience measures include, amongst other things:
The compliance audit under the KRITIS umbrella legislation is currently being specified
With TÜV Nord’s KRITIS compliance assessment services, you can demonstrate that all requirements have been implemented transparently and in accordance with the regulations. Please feel free to contact us for further information.
The BSI requires operators of critical infrastructure to meet certain requirements. Here is an overview of the measures to be implemented:
Companies must register with the BSI and designate a contact point immediately upon being identified as a KRITIS operator. The BSI may register operators as critical infrastructure on its own initiative and, in certain circumstances, request access to documents if they fail to comply with their registration obligation.
Under IT-SiG 2.0, intrusion detection systems (IDS) are now explicitly included among the technical and organisational security measures in KRITIS facilities. These systems must continuously and automatically collect and analyse appropriate parameters and characteristics from ongoing operations. To this end, they should be capable of continuously identifying and preventing threats, as well as providing for appropriate remedial measures in the event of incidents. This requirement can be met, for example, through a Security Operations Centre (SOC) or Security Information and Event Management (SIEM).
The use of SzA will be mandatory from 1 May 2023 at the latest.
Operators of critical infrastructure and organisations of particular public interest are required, in the event of significant disruptions, to provide the BSI, upon request, with the information necessary to resolve the disruption.
Companies must report the use of critical components in certain sectors. The use of such components may be prohibited. According to Section 2 of the IT Security Act (IT-SiG), critical components are IT products whose failure would significantly impair the functioning of the system. These components are yet to be defined for the respective sectors.
Operators must compile an inventory of critical IT products in KRITIS facilities — including up-to-date information on manufacturers and product types. Until now, this requirement applied only to the telecommunications KRITIS sector.
The KRITIS protection objectives (availability, confidentiality, integrity and authenticity) must be defined on the basis of the operationally relevant components, incorporated into the risk assessment and taken into account throughout all processes. The impact on the operational capability of the critical infrastructure and the critical service should serve as a guide to the extent of the risk to the general public.
If security measures are feasible and appropriate according to the current state of the art, the operator must implement them. As a general rule, transferring risks – for example, to insurance companies – is not possible and is no substitute for security measures.
A purely business-oriented risk assessment is generally insufficient.
In accordance with Section 8a(3) of the Federal Information Security Act (BSIG), operators of critical infrastructure must demonstrate to the Federal Office for Information Security (BSI) every two years, through security audits, that they have implemented appropriate measures and are complying with technical standards.
Regardless of whether they are classified as critical infrastructure, the relevant facilities and organisations are subject to numerous regulations. Consequently, depending on the sector, different responsibilities and exemptions apply under the BSIG and the KRITISDachG, which are intended to prevent duplication of regulation. Here are a few examples.
KRITIS operators in the financial sector are subject to supervision by the Federal Financial Supervisory Authority (BaFin). Exceptions to the requirements of the BSIG arise, amongst other things, in connection with the Digital Operational Resilience Act (DORA), which already sets out strict requirements in the areas of risk management, incident reporting, audit and documentation obligations, and supply chain management.
The Federal Network Agency (BNetzA) is responsible for operators of public telecommunications networks and providers of publicly available telecommunications services. In this sector, the Telecommunications Act (TKG) sets out, amongst other things, exceptions to the scope of the BSIG.
The Federal Network Agency (BNetzA) is also responsible for operators of energy supply networks, energy installations and digital energy services. In this regard, the Energy Industry Act (EnWG) limits the scope of application of the BSIG.
There are also overlaps between the two key pieces of legislation – the BSI Act and the KRITIS Framework Act – and therefore a need to clarify their respective scopes. The BSI Act distinguishes between important organisations and particularly important organisations:
Particularly important organisations are those in seven sectors which have at least 250 employees or an annual turnover of 50 million euros and a balance sheet total of more than 43 million euros. KRITIS operators are automatically classified as particularly important organisations.
Whilst important organisations are not KRITIS organisations, they must nevertheless comply with requirements regarding information and physical security. These are companies in seven sectors with at least 50 employees or an annual turnover and total assets of more than 10 million euros.
The requirements of the BSIG generally distinguish between important facilities and particularly important facilities. Within the category of particularly important facilities, a further distinction is made. Classification may be based either on the operation of critical installations or on the thresholds set out in Section 28 of the BSIG.
The following table provides an overview of the requirements arising from the BSIG and sets these out against the respective categories of facilities.
The implementation of an Information Security Management System (ISMS) is mandatory for operators of critical infrastructure in order to comply with the new security standards. An ISMS does not merely relate to a company’s IT security, but also helps to optimise business processes and structures in order to reduce disruptions and risks relating to information security management.
KRITIS operators can, for example, meet the BSI’s requirements by obtaining certification in accordance with ISO 27001, incorporating the additional aspects of the KRITIS protection objectives as set out in Section 8a of the BSIG.
Another option for providing evidence is to use a sector-specific security standard (B3S) recognised by the BSI or the BSI’s guidance document as the basis for assessment.
| BSIG | Contents | Critical infrastructure (KRITIS) | Particularly important entity (excluding KRITIS) | Important entity |
|---|---|---|---|---|
| §30 | Risk management measures | Applicable | Applicable | Applicable |
| §31 | Specific requirements for risk management | Applicable | Not applicable | Not applicable |
| §32 | Reporting obligations | Applicable | Applicable | Applicable |
| §33 | Registration requirements | Applicable | Applicable | Applicable |
| §34 | Special registration requirements | Applicable | Not applicable | Not applicable |
| §35 | Duty to provide information | Applicable | Applicable | Applicable |
| §38 | Duties of the management | Applicable | Applicable | Applicable |
| §39 | Duties to provide evidence | Applicable | Not applicable | Not applicable |
| §41 | Prohibition on the use of critical components | Applicable | Not applicable | Not applicable |
| §61 | Supervisory and enforcement measures by the Federal Ministry for Economic Affairs and Energy (BwE) | Not applicable | Applicable | Not applicable |
| §62 | Supervisory and enforcement measures wE | Not applicable | Not applicable | Applicable |
KRITIS and NIS2 are not alternatives, but rather sets of regulations that build on one another. KRITIS traditionally refers to the approximately 2,000 operators of critical infrastructure in nine sectors with high sector-specific thresholds, regulated by the BSI-KritisV. NIS2, implemented in the new BSIG (in force since 6 December 2025), covers significantly more organisations: around 29,500 essential and important facilities across 18 sectors. KRITIS operators form a subset of those affected by NIS2 — they must comply with both the NIS2 obligations under Sections 30 and 31 of the BSIG and the additional KRITIS-specific obligations (Section 39 of the BSIG, verification of compliance) and the KRITIS umbrella law.
The KRITIS Framework Act (Act Implementing the CER Directive) came into force in March 2026 and strengthens the physical resilience of critical infrastructure — complementing the cybersecurity requirements of the BSIG. It obliges operators of critical facilities to carry out risk analyses, implement physical protection measures, manage emergencies and crises, and report serious incidents to the Federal Office for Civil Protection and Disaster Assistance (BBK). In practical terms, this means that KRITIS operators must register with two authorities: the BSI for cyber security and the BBK for physical resilience.
Since 6 December 2025, the new BSIG has applied to around 29,500 companies across 18 sectors. This applies to medium-sized and large companies with 50 or more employees or an annual turnover of 10 million euros in sectors such as energy, water, healthcare, transport, digital infrastructure, finance and insurance, and municipal waste management. Traditional KRITIS operators are automatically classified as particularly important facilities and are subject to the strictest requirements. You can check whether a company is affected using the BSI impact assessment on the BSI portal.
KRITIS operators are obliged to provide evidence to the BSI every three years that they comply with the security requirements set out in Sections 30 and 31 of the BSIG. This verification may be provided by means of an audit, certification or inspection — ISO/IEC 27001 certification, supplemented by additional assessment criteria carried out by a DAkkS-accredited body, is recognised as a valid basis. Since April 2025, the requirements have been set out in binding detail in two BSI documents: the GAiN (Basic Requirements for the Verification Process, Version 2.2) and the RUN document (Maturity and Implementation Level Assessment), which prescribes defined maturity levels for ISMS, BCMS and intrusion detection systems (SzA).
KRITIS operators are subject to a tiered reporting obligation: significant security incidents must be reported to the BSI within 24 hours as an early warning and within 72 hours in the form of a full report. A final report must be submitted within one month at the latest. Furthermore, the KRITIS Framework Act requires serious physical incidents to be reported to the BBK. Breaches of the reporting obligations may result in fines of up to 10 million euros or 2 per cent of global annual turnover.
TÜV NORD CERT is an internationally recognised and reliable partner for testing and certification services. Our experts and auditors possess in-depth knowledge and are all permanently employed by TÜV NORD. This ensures independence, impartiality and continuity in the support we provide to our clients. The benefit for you is clear: our auditors guide and support the development of your business and provide you with objective feedback.